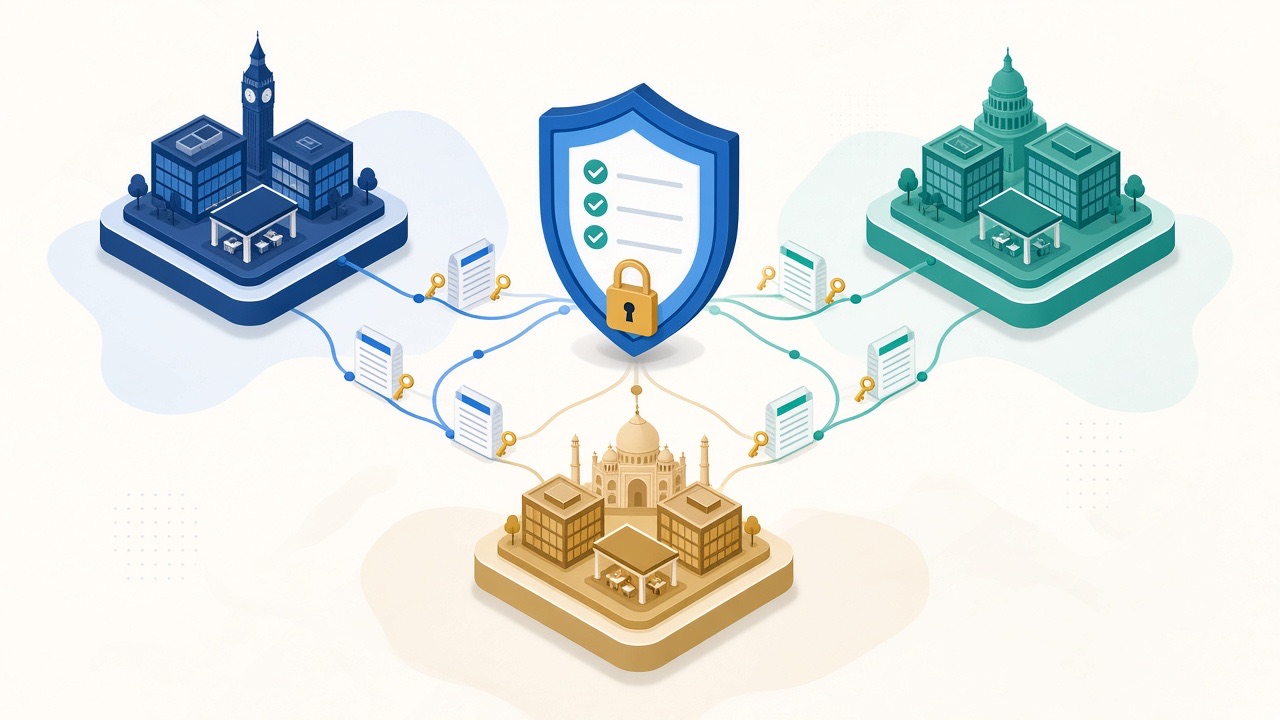
Security and privacy teams are exhausted by duplicate evidence requests. India delivery centres amplify the problem because data flows, subprocessors, and access patterns span jurisdictions. The enterprise cost is not only audit fees; it is slower releases, shadow IT workarounds, and brittle trust with customers who see inconsistency in your answers.
The business problem: audit theatre versus operational truth
When controls exist only in slide decks, auditors find gaps, and engineering pays in freeze windows. When controls exist in operations but are documented three different ways, you pay in people time. The goal is a single operational truth with multiple compliant “lenses” for different regulators.
Practical framework: map once, reuse everywhere
We map SOC 2 trust services criteria alongside India DPDP obligations and UK/EU processor duties in one matrix. Evidence is collected once: access reviews, encryption posture, subprocessors, material data protection impact assessments, and breach rehearsal notes. Your security organisation receives one quarterly pack that can be sliced for each audience without rework.
| Operational control | SOC 2 lens | India / UK-EU lens |
|---|---|---|
| Access reviews quarterly | CC6 logical access | Processor accountability + least privilege |
| Encryption in transit and at rest | CC6 data protection | Security safeguards + breach readiness |
| Subprocessor governance | CC9 vendor risk | Transparency + DPA flow-downs |
Customers do not reward three different stories about how you handle access. They reward one story that survives scrutiny in London, New York, and Bengaluru.
Strategic recommendations
Fund a controls owner who sits between security, legal, and platform engineering, not a rotating committee. Publish a RACI for evidence refresh. Run joint tabletop exercises that include India leadership as decision-makers, not note-takers. And treat customer questionnaires as derivative outputs of your internal truth, not the source of truth.
Evidence that holds up in an audit
Auditors and enterprise customers ask for evidence, not intentions. The most efficient approach is to generate evidence as a by-product of normal work: access requests and approvals in the identity system, change records in the delivery pipeline, device compliance from endpoint management, and training completion from the learning platform.
When evidence lives in the systems people already use, preparing for a review becomes a matter of exporting and sampling rather than chasing screenshots. Assign one owner per control family, keep a simple register that maps each control to its evidence source, and test a sample every quarter rather than once a year.
Where cross-border programmes usually slip
The gaps tend to appear at the joins. Joiner and leaver processes that work at headquarters but lag for India staff. Customer data copied into lower environments for convenience. Shared accounts created during a busy launch and never removed. Vendor tools adopted locally without passing through procurement and security review.
None of these require new policy; they require the same controls to apply everywhere. Run access reviews across all sites together, apply one data-handling standard to every environment, and route new tools through one intake process. The goal is a framework that looks identical whether an auditor samples London, New York, or Bengaluru.
Closing
Compliance maturity in GCC programmes is measured by release cadence under scrutiny, not by binder thickness. The companies that do this well tell one operational story, then prove it with the same artefacts regulators, customers, and their own engineers already use.
Working through this in your own GCC plan?
We will give a direct answer on a short call.